Our research team has discovered a vulnerability in the "open62541" OPC UA library for industrial control systems!
Recently, members of our research team discovered a vulnerability in “open62541,” an open-source library for the “OPC UA” communication standard used in industrial control systems (OT/ICS), and contributed to the development team’s efforts to fix it.
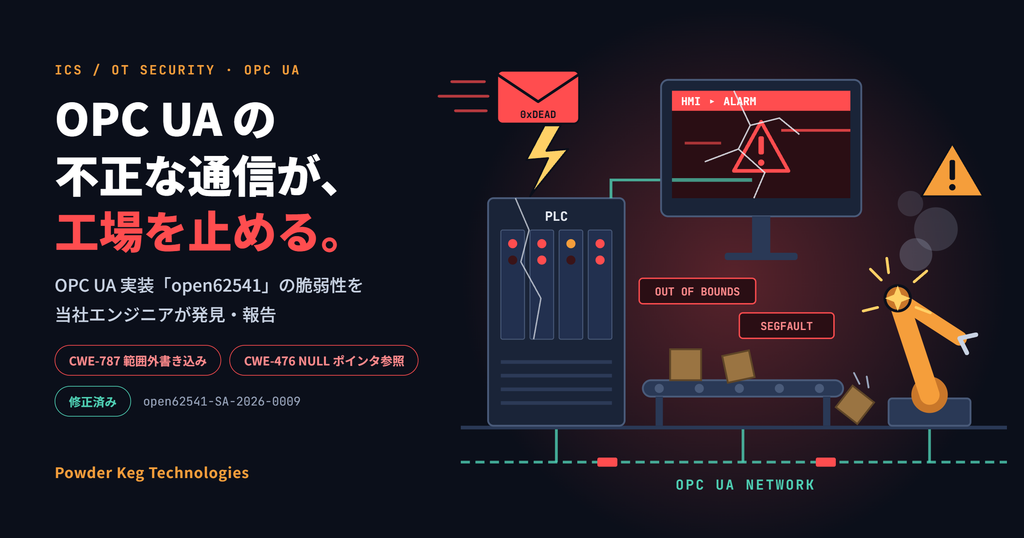
The vulnerability discovered this time relates to data processing in OPC UA PubSub communication and could cause memory corruption or process crashes under certain conditions.
A fix for this vulnerability was merged into the official open62541 GitHub repository on July 10, 2026.
The open62541 vulnerability(open62541-SA-2026-0009)
Affected Software: open62541
Affected Protocol: OPC UA (OPC Unified Architecture)
Affected Functionality: Processing of NetworkMessages in PubSub communication
Vulnerability Type: Out-of-bounds write (CWE-), NULL pointer dereference
Potential Impact: Memory corruption, process crash
Vulnerability Information: open62541-SA-2026-0009
Fix Date: July 10, 2026 (Pull Request merge date)
Fix Information: open62541 GitHub Pull Request #8181
What Are open62541 and OPC UA?
OPC UA (Open Platform Communications Unified Architecture) is a communication standard used to exchange data between factory production equipment, industrial control devices, and supervisory control systems.
It is utilized across a wide range of industrial sectors, including manufacturing, and is one of the key technologies for connecting PLCs (programmable logic controllers), industrial PCs, SCADA systems, and various IoT devices.
"open62541" is an open-source library that implements OPC UA; it is used for developing OPC UA servers and clients, as well as for embedding communication capabilities into industrial devices.
In recent years, as factories and production facilities have become increasingly networked, it has become increasingly important to implement countermeasures against cyberattacks targeting OT environments.
In particular, in industrial control systems, security issues that cause equipment or systems to shut down can impact production activities and facility operations. Therefore, it is important to investigate vulnerabilities inherent in the implementation of communication protocols and verify their security.
Vulnerability discovered in open62541
The vulnerability discovered this time relates to the processing of NetworkMessages used in OPC UA PubSub communication.
PubSub (Publish-Subscribe) is a communication method in which the sender and receiver of data exchange information via messages.
In open62541, validation for certain input values was insufficient when processing data related to this communication.
Specifically, in the UA_NetworkMessage_makeSyntheticPayloadHeader() function, there is a process that writes data to a fixed-length array based on the number of metadata elements; however, there was insufficient checking to prevent values exceeding the array’s upper limit from being specified.
As a result, under certain conditions, out-of-bounds writing to the array may occur, potentially leading to memory corruption.
Additionally, if a pointer referencing metadata was NULL, no appropriate checks were performed, and the process could crash due to a NULL pointer reference.
We worked with the development team for open62541 to fix these issues.
This vulnerability stems not from the OPC UA communication specification itself, but from the data processing performed by the software that implements that specification.
The Importance of Vulnerability Assessments in OT and Industrial Control Systems
In OT environments used in factories and production facilities, unlike in IT environments, system availability and stable operation are considered particularly important. Consequently, unlike with IT systems, not only are RCE vulnerabilities given the highest priority, but vulnerabilities that cause system outages—such as DoS vulnerabilities—are also classified as critical-level vulnerabilities in OT systems.
In OT environments, there is equipment that operates for extended periods and devices for which software updates are not easily performed; consequently, vulnerable software that has been deployed may remain in use for a long time.
When implementing security measures for control system protocols, it is important not only to ensure network segmentation and access control but also to verify the security of the software that processes communications.
As seen with the recent open62541 vulnerability, there are cases where a vulnerability may not manifest during normal use but can be triggered by unexpected input or abnormal communication data.
Therefore, in addition to vulnerability assessments based on known CVEs, fuzzing of communication protocol implementations and security verification to discover unknown vulnerabilities are also effective measures.
Security Assessment of OT and Control Systems by MUSHIKAGO
Our company has extensive experience conducting vulnerability assessments and penetration tests not only for IT environments but also for OT and industrial control systems, including factories and manufacturing equipment. We have team members with extensive hands-on experience in OT, and we provide services tailored to the specific needs of each organization.
"MUSHIKAGO," a hardware-based security testing device developed and provided by our company, is a security product designed to visualize devices on a network and identify vulnerabilities and attack risks.
In particular, a key feature is its ability to operate in OT environments—such as factories with restricted internet access or closed networks (including completely offline environments).
It also supports proprietary control protocols and is used to enhance product security during the manufacturing process (using features such as MUSHIKAGO’s fuzzing capabilities).
- Quickly visualize devices within the enterprise
- Detect security risks for each device
- Supports closed environments (factories, OT/ICS) without requiring an internet connection
- Selected by the Ministry of Economy, Trade and Industry (METI) as a domestically produced security product
If your company is looking to “gain a detailed understanding of your network and device status,” “verify that your environment is truly free of risks,” or “is considering penetration testing for the first time,” please feel free to contact us.
Click here for more information about MUSHIKAGO or to contact us
https://powderkegtech.com/mushikago/
参考
open62541 GitHub:Pull Request #8181
Archive
- November 2026
- October 2026
- August 2026
- June 2026
- April 2026
- March 2026
- November 2025
- October 2025
- September 2025
- June 2025
- March 2025
- February 2025
- October 2024
- August 2024
- May 2024
- April 2024
- March 2024
- February 2024
- November 2023
- October 2023
- April 2023
- September 2022
- August 2022
- July 2022
- June 2022
- April 2022
- March 2022
- December 2021
- October 2021
- August 2021